Web Design
How to Register a .com.au Domain
How to get a .com.au domain: eligibility, choosing a name, registering it, WHOIS privacy and the .au direct option if you have no ABN.
Your web developer or project manager should assess the security needs of your website.
If your website is complex or you are wanting an application or software, then your developer will need to do a security threat model. Which is a task that looks at cyber security risks then uses that understanding to protect systems in a risk based way.
Security should be proportionate to the needs of the specific website. The investment in security should match the security threat model.
Data loss or out-of-commission websites can turn away potential customers. Partnering with an effective hosting provider can keep your site online and secure, which is critical to any business.
A good relationship with your hosting provider and web developer is a must.
It is important to have experienced and supportive tech support. Make sure they are available if your website experiences an outage. Ideally that means support 24 hours a day, 365 days a year.
Phone support is great, but make sure they offer online support too. Online conversations are helpful because you keep a written record of what the hosting provider promised and delivered.
A good hosting plan will offer instant access to all server logs within the past 24 hours on the server. This data includes server errors and user access records along with a host of additional data, and can be used to pinpoint security issues.
Backups are the quickest way to restore a hacked website. Data backups are a standard for every hosting provider; how often your site is backed up depends on the hosting plan and your needs.
You can also take your own backup of the website and store it on a remote or portable hard drive. Although this may be seen as overkill, it does allow the website owner the ability to move the website rapidly to a new hosting platform if the current host is compromised.
Some tips for managing your own back ups:
You may have noticed that some websites have http in the URL while others have https. The extra “s” stands for secure and indicates that it has an SSL and the website is secure.
SSL is the standard security technology for establishing an encrypted link between a web server and a browser. This link ensures that all data passed between the web server and browser remain private.
SSL safeguards your data and enables secure sessions once the certificate is installed on the web server. Users can see whether or not a website is secure by looking at the browser tab: if the address starts with https and the browser shows a padlock or site settings icon, the connection is encrypted.
Your hosting provider can include an SSL in your hosting plan.
Dive deeper: What is SSL and why do I need it
If your site still runs on http, switching is worth doing: browsers flag http pages as “not secure”, and Google has used HTTPS as a lightweight ranking signal since 2014. The switch itself needs care, because a half-finished move can cost you rankings:
Google’s guide to moving a site with URL changes covers the detail. If you’d rather not do it yourself, your web developer or care plan provider can handle it.
By default, your WordPress site’s login URL is domain.com/wp-admin. Hackers know this and can use it to easily get access to your site and cause mayhem.
To protect yourself from these attacks, you should rename your admin folder (instructions can be found via the link below).
Dive deeper: How to Find Your WordPress Login URL (Change It, Lock It Down)
Anyone with access to your website should have only the access privileges that are essential to that user’s work, and nothing more.
For example, if someone wants to write a guest blog post for you, make sure their account does not have full administrator privileges. They should only be able to create new posts and edit their own posts because there is no need for them to be able to change website settings.
Granting privileges to specific roles will guide what that individual can and cannot do. In a perfect system, a role will stop anyone who tries to perform an action beyond what it’s designed for. This approach can preserve your business’ online presence and prohibit devastating setbacks.
Once you have separate accounts for every user, you can log user activity and keep an eye on when and where they normally access the website. This way, if a user logs in at an odd hour or from a suspicious location, you can investigate, then confirm and act if the account has been compromised.
Automated attacks try usernames and passwords on websites all day, every day. Secure usernames and passwords make those attacks far less likely to succeed.
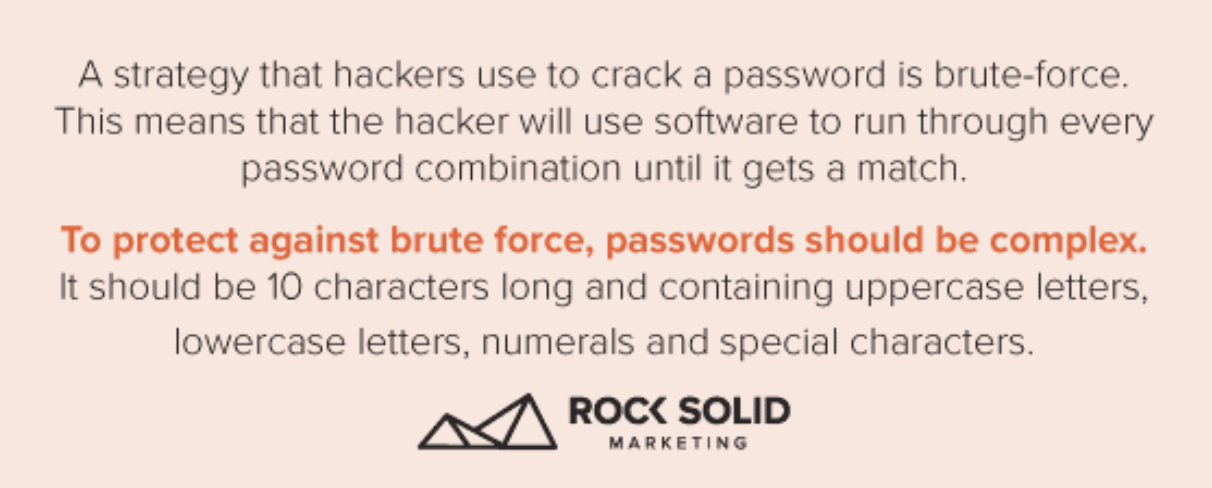
A strategy that hackers use to crack a password is brute-force. This means that the hacker will use software to run through every password combination until it gets a match.
To protect against brute force, passwords should be complex: at least 10 characters long, with uppercase letters, lowercase letters, numerals and special characters.
Consider using two-factor authentication, which asks users to log in by using a two-step user identification method. The first one is the username and password and the second step requires you to identify that you are who you say you are by obtaining authentication credentials by using a separate device or app.
We also recommend you restrict the amount of login attempts made by users. A maximum of 5 password guesses per minute and a maximum of 2 password resets per account, should suffice. This allows for the case when someone forgets their password. It will also halt brute-force attacks.
The number of guesses per IP address could be a greater number. This is because shared offices might use the same IP address and have multiple users trying to log in on your website. If you notice a high volume of login attempts from the same IP address frequently, you might need to investigate and/or make the executive decision to block that IP. We suggest 20 guesses per minute and a maximum of 5 password resets.
You might also like to look at password management tools that randomly generate your passwords for you and store them safely.
Software updates help keep hackers out.
Hackers aggressively target security flaws in popular web software, apps, plugins and programs. As such, all of these need to be updated frequently to patch any identified security weaknesses.
Much like with changing the oil in your car, computers and the software they use need regular updates to ensure they continue to run safely. Keeping your software updated will repair any identified security flaws and fix or remove computer bugs. In fact, many software updates exist because a security flaw has been found and fixed.
Keeping on top of updates will save you a lot of stress and time in the future when hackers decide they want to take advantage of any new vulnerability on your site.
For WordPress, there are many WordPress security plugins that will add a firewall and run security audits that will flag your vulnerabilities so you can prevent attacks.
Keep it simple.
Which is more secure, the house with 20 doors or the house with 1 door? The answer is obviously 1 door. The more complex a system becomes, the harder it is to secure.
Unnecessary complexity is a security liability. To reduce this risk, keep your website as simple as possible. Every plugin you install on your website increases your “attack surface”. The more code you are running, the higher the odds of a security vulnerability.
Every plugin you add to your site also represents another developer you are relying on to keep you safe. That includes writing secure code, responding quickly to vulnerability reports and keeping your best interests in mind. It is also important to have only one theme downloaded and activated on your site.
Choose trustworthy plugins.
Security issues in plugins are a common way into WordPress sites. Choose plugins that are frequently updated, at least within the past two months, and are operating on the latest version of WordPress. To make sure security is addressed, examine the plugin’s change log for details on the changes made to each new version.
Other indicators of a secure plugin are a high download count and good reviews. Also check out what support they offer. Good support means that you can ask any question and get a helpful answer, quickly. If the developer has a strong reputation and puts out good products, chances are that any plugin from them will be good.
This also follows through to applications on your mobile devices. Once you have checked that an application is legitimate, be vigilant in checking application permissions. Any permissions that are not required for the application to work properly, should be turned off as they could be questionable spyware.
Your website will likely have plugins, apps and software that will also require maintenance and updates. At least once a week, your website should be scanned for updates. This could be time consuming if you have a complex site.
A good web host or developer will take on these updates for you or help you with the process.
Attackers continue to target old plugins with known vulnerabilities in malware campaigns aimed at WordPress websites.
A nulled WordPress theme is a pirated theme. They are also called “checked themes” or “hacked themes”. They are themes that someone hacks or even gets legally and shares them with others without the seller’s permission.
They are a common way of getting malware or malicious code on your website. If you want to learn the process of removing viruses from your website, download a nulled theme.
It is common for beginners to download free themes without knowing they are nulled. They find websites that offer free premium themes, but a genuine premium theme is only free when the developer offers it on their own site.
Some nulled themes may be safe but unless you have the knowledge and time to dig through all the code, you have no idea what else is lurking for you in the nulled extension. At Rock Solid Marketing, we don’t use nulled themes, not only because of the safety issue but for ethical reasons. Nulled themes deprive the developer of funds and are offensive to the web development industry.
It is much better to download themes from the author’s website or from the official WordPress themes repository. There are also legitimate sites such as TemplateMonster.
Many people install plugins, programs and services, decide not to use them, then forget about uninstalling them. Regularly checking for updates should bring these to your attention.
Remember every program and service or plug in on your site is a security vulnerability that could put your site in danger.
The less you have installed the more secure your website will be.
Audit and disable features on your website you are not benefiting from. For example: disable commenting on your website if you are not getting value from that service.
This should also be followed through to computer software. Malware is known to jump from an infected user’s computer through text editors and FTP clients. If a security attack gets into your computer, it not only affects your machine, but the hackers can get full access to websites when webmasters are logged into their admin interfaces.
If you aren’t sure of the purpose of a specific application, do some research to decide whether you need it or not.
If you don’t intend to use it, remove it.
Pro tip: Keep your file structure organised to keep track of changes and make it easier to delete old files.
Public wifi allows users to use the internet in a public place, such as a library, coffee shop or airport. The problem is that you can’t be sure how secure these networks are.
Steps you can take to stay safer on a public shared wifi include:
On public wifi, avoid these:
Dive deeper: How to Avoid Public WiFi Security Risks
Act quickly and calmly. If someone looks after your website for you, call them first: a recent backup is often the fastest way back. If you manage the site yourself, the usual order is:
Our guide to what to do when your website has been hacked walks through each step. A firewall service such as Cloudflare, or a security plugin with a firewall, can help stop the same attack happening again.
Yes. If finding time for updates and backups is the hard part, a website care plan hands that work to a team that does it every month. Missed maintenance is a common way in for attackers: old plugins and themes with known security holes stay on the site, and the longer updates wait, the higher the risk.
Rock Solid Marketing’s website care plans start from $275 + GST a month (minimum 6 months). The Basic plan covers framework and plug-in updates, backups, security checks and content maintenance for 3 to 5 page sites. Bigger sites suit Essentials ($395 + GST a month), and online stores and complex sites suit Premium ($549 + GST a month).
A monthly plan usually costs much less than cleaning up or rebuilding a hacked site, before you count the lost enquiries while it’s down. If you’re happy to do the updates yourself, the 14 steps above are the place to start.
Every website is vulnerable to cyber attack. It is the responsibility of every website owner to take the necessary precautions to reduce the likelihood of an attack.
Be proactive when it comes to protecting your company’s and customers’ data. It is a good idea to have web safety policies in place and teach your employees to be safe online. One single cyber attack could ruin your reputation and even your business, so it’s okay to be slightly paranoid when it comes to protecting against cyber attacks as it is the security of your business that is at stake.
Whether your site takes online payments or personal information, the data visitors enter into your site must land in the right hands.
If your website is targeted by hackers, a good first response is to stay calm, reset your passwords, and run a scan to detect any malware. You should also contact your web host if you need help with any issues.
A marketing team that has helped businesses across Sunraysia and the Mallee since 2017, from our office on Deakin Avenue in Mildura.
Keep reading
How to get a .com.au domain: eligibility, choosing a name, registering it, WHOIS privacy and the .au direct option if you have no ABN.
A plain-English guide to WCAG 2.2: what the guidelines say, what Level AA means, whether it is required in Australia and how to check your website.
Shopify or WooCommerce? A fair comparison of costs, transaction fees, hosting, speed, SEO and control, and how to decide which suits your store.

Let’s start by scheduling a free discovery call so we can get to know each other and see if we’re a good fit for your marketing needs.